I've updated our NSM package and the new package version is:
securityonion-nsmnow-admin-scripts - 20120724-0ubuntu0securityonion91
Issues Resolved
Issue 620: NSM: stop netsniff-ng only after checking all interfaces for pcaps to delete
https://code.google.com/p/security-onion/issues/detail?id=620
Issue 647: NSM: rotate netsniff-ng.log
https://code.google.com/p/security-onion/issues/detail?id=647
Issue 597: nsm_all_del_quick: delete /nsm/bro/logs and /nsm/bro/extracted
https://code.google.com/p/security-onion/issues/detail?id=597
Issue 595: NSM: prevent Bro version warning
https://code.google.com/p/security-onion/issues/detail?id=595
Issue 611: nsm_sensor_clean: replace server with sensor
https://code.google.com/p/security-onion/issues/detail?id=611
Updating
The new packages are now available in our stable repo. Please see the following page for full update instructions:
https://code.google.com/p/security-onion/wiki/Upgrade
Thanks
Thanks to the following for testing!
Joe Lane
Ronny Vaningh
David Zawdie
Feedback
If you have any questions or problems, please use our security-onion mailing list:
https://code.google.com/p/security-onion/wiki/MailingLists
Training
Need training? Please see:
https://security-onion-class-20141215.eventbrite.com/
Commercial Support
Need commercial support? Please see:
http://securityonionsolutions.com
Help Wanted
If you and/or your organization have found value in Security Onion, please consider giving back to the community by joining one of our teams:
https://code.google.com/p/security-onion/wiki/TeamMembers
We especially need help testing new packages:
http://groups.google.com/group/security-onion-testing
Thanks!
Monday, November 17, 2014


Tuesday, November 11, 2014
Argus 3.0.8 packages now available!
Argus 3.0.8 was recently released:
http://qosient.com/argus/
I've updated our Argus packages and the new package versions are as follows:
securityonion-argus-server - 3.0.8-0ubuntu0securityonion1
securityonion-argus-clients - 3.0.8-0ubuntu0securityonion2
Issues Resolved
Issue 382: Update Argus packages
https://code.google.com/p/security-onion/issues/detail?id=382
Release Notes
Please note that raips and raplot are no longer installed by default and this is by design according to Carter Bullard:
http://article.gmane.org/gmane.network.argus/10830
Updating
The new packages are now available in our stable repo. Please see the following page for full update instructions:
https://code.google.com/p/security-onion/wiki/Upgrade
Thanks
Thanks to the following for testing!
Eddy Simons
David Zawdie
Feedback
If you have any questions or problems, please use our security-onion mailing list:
https://code.google.com/p/security-onion/wiki/MailingLists
Training
Need training? Please see:
https://security-onion-class-20141215.eventbrite.com/
Commercial Support
Need commercial support? Please see:
http://securityonionsolutions.com
Help Wanted
If you and/or your organization have found value in Security Onion, please consider giving back to the community by joining one of our teams:
https://code.google.com/p/security-onion/wiki/TeamMembers
We especially need help in answering support questions on the mailing list:
http://groups.google.com/group/security-onion
We also need help testing new packages:
http://groups.google.com/group/security-onion-testing
Thanks!
$400 Early Bird discount for 3-day Security Onion Training Class in Augusta GA
Our 3-day Security Onion training class will be in Augusta GA next month. If you register by Friday November 21, you can use the following discount code for $400 off!
early-bird-57912
For more details and to register, please see:
https://security-onion-class-20141215.eventbrite.com/
If you have any questions, please use the Contact link on the bottom of the Eventbrite page.
early-bird-57912
For more details and to register, please see:
https://security-onion-class-20141215.eventbrite.com/
If you have any questions, please use the Contact link on the bottom of the Eventbrite page.
Wednesday, October 29, 2014
Sguil 0.9 and Squert 1.5.0 now available!
Sguil 0.9 and Squert 1.5.0 were recently released:
http://sourceforge.net/p/sguil/mailman/message/32230854/
http://www.squertproject.org/summaryofchangesforsquertversion130
http://www.squertproject.org/summaryofchangesforsquertversion140
http://www.squertproject.org/summaryofchangesforsquertversion150
I've updated our packages to include both of these releases. The new package versions are as follows:
securityonion-capme - 20121213-0ubuntu0securityonion20
securityonion-http-agent - 0.3.1-0ubuntu0securityonion6
securityonion-nsmnow-admin-scripts - 20120724-0ubuntu0securityonion88
securityonion-ossec-rules - 20120726-0ubuntu0securityonion4
securityonion-setup - 20120912-0ubuntu0securityonion125
securityonion-sguil-agent-ossec - 20120726-0ubuntu0securityonion4
securityonion-sguil-client - 20141004-0ubuntu0securityonion7
securityonion-sguil-sensor - 20141004-0ubuntu0securityonion7
securityonion-sguil-server - 20141004-0ubuntu0securityonion7
securityonion-squert - 20141015-0ubuntu0securityonion3
Issues Resolved
Issue 287: Sguil 0.9
https://code.google.com/p/security-onion/issues/detail?id=287
Issue 622: Update http_agent for Sguil 0.9 and move from SSL to TLS
https://code.google.com/p/security-onion/issues/detail?id=622
Issue 623: Update ossec_agent for Sguil 0.9 and move from SSL to TLS
https://code.google.com/p/security-onion/issues/detail?id=623
Issue 624: Update CapMe for Sguil 0.9 and move from SSL to TLS
https://code.google.com/p/security-onion/issues/detail?id=624
Issue 625: Update NSM for Sguil 0.9
https://code.google.com/p/security-onion/issues/detail?id=625
Issue 626: Update Setup for Sguil 0.9
https://code.google.com/p/security-onion/issues/detail?id=626
Issue 491: Squert 1.5.0
https://code.google.com/p/security-onion/issues/detail?id=491
Issue 638: securityonion-ossec-rules: add rule to ignore Squert POST
https://code.google.com/p/security-onion/issues/detail?id=638
Release Notes
Please note that the Squert interface has changed quite a bit from the previous version. In particular:
Updating
The new packages are now available in our stable repo. Please see the following page for full update instructions:
https://code.google.com/p/security-onion/wiki/Upgrade
Thanks
Thanks to the following for testing!
Eddy Simons
Mike Pilkington
Landon Lewis
David Zawdie
Feedback
If you have any questions or problems, please use our security-onion mailing list:
https://code.google.com/p/security-onion/wiki/MailingLists
Commercial Support
Need commercial support? Please see:
http://securityonionsolutions.com
Help Wanted
If you and/or your organization have found value in Security Onion, please consider giving back to the community by joining one of our teams:
https://code.google.com/p/security-onion/wiki/TeamMembers
We especially need help in answering support questions on the mailing list:
http://groups.google.com/group/security-onion
We also need help testing new packages:
http://groups.google.com/group/security-onion-testing
Thanks!
http://sourceforge.net/p/sguil/mailman/message/32230854/
http://www.squertproject.org/summaryofchangesforsquertversion130
http://www.squertproject.org/summaryofchangesforsquertversion140
http://www.squertproject.org/summaryofchangesforsquertversion150
I've updated our packages to include both of these releases. The new package versions are as follows:
securityonion-capme - 20121213-0ubuntu0securityonion20
securityonion-http-agent - 0.3.1-0ubuntu0securityonion6
securityonion-nsmnow-admin-scripts - 20120724-0ubuntu0securityonion88
securityonion-ossec-rules - 20120726-0ubuntu0securityonion4
securityonion-setup - 20120912-0ubuntu0securityonion125
securityonion-sguil-agent-ossec - 20120726-0ubuntu0securityonion4
securityonion-sguil-client - 20141004-0ubuntu0securityonion7
securityonion-sguil-sensor - 20141004-0ubuntu0securityonion7
securityonion-sguil-server - 20141004-0ubuntu0securityonion7
securityonion-squert - 20141015-0ubuntu0securityonion3
Issues Resolved
Issue 287: Sguil 0.9
https://code.google.com/p/security-onion/issues/detail?id=287
Issue 622: Update http_agent for Sguil 0.9 and move from SSL to TLS
https://code.google.com/p/security-onion/issues/detail?id=622
Issue 623: Update ossec_agent for Sguil 0.9 and move from SSL to TLS
https://code.google.com/p/security-onion/issues/detail?id=623
Issue 624: Update CapMe for Sguil 0.9 and move from SSL to TLS
https://code.google.com/p/security-onion/issues/detail?id=624
Issue 625: Update NSM for Sguil 0.9
https://code.google.com/p/security-onion/issues/detail?id=625
Issue 626: Update Setup for Sguil 0.9
https://code.google.com/p/security-onion/issues/detail?id=626
Issue 491: Squert 1.5.0
https://code.google.com/p/security-onion/issues/detail?id=491
Issue 638: securityonion-ossec-rules: add rule to ignore Squert POST
https://code.google.com/p/security-onion/issues/detail?id=638
Release Notes
Please note that the Squert interface has changed quite a bit from the previous version. In particular:
- To drill into an event to see the payload of the event, click on the value in the Status (ST) column.
- To generate a full pcap transcript, click on the value in the "Event ID" column.
Updating
The new packages are now available in our stable repo. Please see the following page for full update instructions:
https://code.google.com/p/security-onion/wiki/Upgrade
 |
| Updating packages using "sudo soup" |
 |
| The new OSSEC rules package will prompt you to restart OSSEC |
 |
| The new securityonion-sguil-sensor package will prompt you to restart sensor services |
 |
| The new securityonion-sguil-server package will update your database and import your autocat rules |
 |
| The new securityonion-sguil-server package will then prompt you to restart server services |
 |
| The new securityonion-squert package will update your database |
 |
| Restarting OSSEC using "sudo service ossec-hids-server restart" |
 |
| Restarting server and sensor processes using "sudo service nsm restart" |
 |
| The Sguil client is now updated to 0.9... |
 |
| ...and includes an AutoCat Rule Builder... |
 |
| ...and an AutoCat Viewer |
 |
| Squert has been updated to 1.5.0 |
 |
| Squert Event tab |
 |
| In Squert, you can now pivot to ELSA |
 |
| Pivoting from IP address in Squert to an ELSA query for the IP |
 |
| Squert now allows you to color code IP addresses |
 |
| Color-coded IP address |
 |
| Squert AutoCat Viewer |
 |
| Squert Summary tab including GeoIP mapping |
 |
| Squert Views tab with Sankey Diagram |
Thanks
Thanks to the following for testing!
Eddy Simons
Mike Pilkington
Landon Lewis
David Zawdie
Feedback
If you have any questions or problems, please use our security-onion mailing list:
https://code.google.com/p/security-onion/wiki/MailingLists
Commercial Support
Need commercial support? Please see:
http://securityonionsolutions.com
Help Wanted
If you and/or your organization have found value in Security Onion, please consider giving back to the community by joining one of our teams:
https://code.google.com/p/security-onion/wiki/TeamMembers
We especially need help in answering support questions on the mailing list:
http://groups.google.com/group/security-onion
We also need help testing new packages:
http://groups.google.com/group/security-onion-testing
Thanks!
Tuesday, October 28, 2014
New securityonion-web-page package fixes an issue in the Apache configuration
Yesterday, we released a new version of the securityonion-web-page package:
http://blog.securityonion.net/2014/10/new-securityonion-web-page-and.html
That package updated the Apache configuration to disable SSLv3. However, the package used "sed" to update /etc/apache2/mods-enabled/ssl.conf, which is a symlink to /etc/apache2/mods-available/ssl.conf. When sed operates on a symlinked file, it replaces the symlink with a copy of the file and then makes its modifications. The broken symlink would have caused issues with future package updates, so I've released a new version of the securityonion-web-page package that fixes the symlink and updates the original file properly.
The new package version is as follows:
securityonion-web-page - 20141015-0ubuntu0securityonion7
Issues Resolved
Issue 640: securityonion-web-page: previous update broke ssl symlink
https://code.google.com/p/security-onion/issues/detail?id=629
Updating
The new packages are now available in our stable repo. Please see the following page for full update instructions:
https://code.google.com/p/security-onion/wiki/Upgrade
Thanks
Thanks to David Zawdie for testing!
Feedback
If you have any questions or problems, please use our security-onion mailing list:
https://code.google.com/p/security-onion/wiki/MailingLists
Commercial Support
Need commercial support? Please see:
http://securityonionsolutions.com
Help Wanted
If you and/or your organization have found value in Security Onion, please consider giving back to the community by joining one of our teams:
https://code.google.com/p/security-onion/wiki/TeamMembers
We especially need help in answering support questions on the mailing list:
http://groups.google.com/group/security-onion
We also need help testing new packages:
http://groups.google.com/group/security-onion-testing
Thanks!
http://blog.securityonion.net/2014/10/new-securityonion-web-page-and.html
That package updated the Apache configuration to disable SSLv3. However, the package used "sed" to update /etc/apache2/mods-enabled/ssl.conf, which is a symlink to /etc/apache2/mods-available/ssl.conf. When sed operates on a symlinked file, it replaces the symlink with a copy of the file and then makes its modifications. The broken symlink would have caused issues with future package updates, so I've released a new version of the securityonion-web-page package that fixes the symlink and updates the original file properly.
The new package version is as follows:
securityonion-web-page - 20141015-0ubuntu0securityonion7
Issues Resolved
Issue 640: securityonion-web-page: previous update broke ssl symlink
https://code.google.com/p/security-onion/issues/detail?id=629
Updating
The new packages are now available in our stable repo. Please see the following page for full update instructions:
https://code.google.com/p/security-onion/wiki/Upgrade
 |
| Updating using "sudo soup" |
 |
| Verifying that the update fixed the ssl.conf hyperlink |
 |
| Verifying that SSLProtocol excludes SSLv3 |
 |
| Restarting Apache using "sudo service apache2 restart" |
 |
| Verifying that SSLv3 is disabled using "openssl s_client -connect localhost:443 -ssl3" |
Thanks
Thanks to David Zawdie for testing!
Feedback
If you have any questions or problems, please use our security-onion mailing list:
https://code.google.com/p/security-onion/wiki/MailingLists
Commercial Support
Need commercial support? Please see:
http://securityonionsolutions.com
Help Wanted
If you and/or your organization have found value in Security Onion, please consider giving back to the community by joining one of our teams:
https://code.google.com/p/security-onion/wiki/TeamMembers
We especially need help in answering support questions on the mailing list:
http://groups.google.com/group/security-onion
We also need help testing new packages:
http://groups.google.com/group/security-onion-testing
Thanks!
Monday, October 27, 2014
New securityonion-web-page and securityonion-elsa-extras packages provide more SSL visibility
A vulnerability in SSLv3 was recently announced (nicknamed POODLE):
http://googleonlinesecurity.blogspot.com/2014/10/this-poodle-bites-exploiting-ssl-30.html
http://www.wired.com/2014/10/poodle-explained/
https://isc.sans.edu/diary/OpenSSL%3A+SSLv3+POODLE+Vulnerability+Official+Release/18827
https://www.imperialviolet.org/2014/10/14/poodle.html
In response to this, we recently added some SSLv3 queries:
http://blog.securityonion.net/2014/10/new-securityonion-web-page-package-adds.html
Today, we're adding some additional ELSA queries to allow you to see your SSL traffic grouped by version or by cipher.
Today's update will also reconfigure Security Onion's Apache instance to no longer accept connections using SSLv3.
The new package versions are as follows:
securityonion-elsa-extras - 20131117-1ubuntu0securityonion45
securityonion-web-page - 20141015-0ubuntu0securityonion2
Issues Resolved
Issue 629: securityonion-web-page: disable SSLv3 in Apache ssl.conf
https://code.google.com/p/security-onion/issues/detail?id=629
Issue 627: securityonion-web-page: separate syslog-ng into program and host queries
https://code.google.com/p/security-onion/issues/detail?id=627
Issue 631: securityonion-web-page: collapse query categories by default
https://code.google.com/p/security-onion/issues/detail?id=631
Issue 634: securityonion-web-page: add queries for ssl_version and ssl_cipher
https://code.google.com/p/security-onion/issues/detail?id=634
Issue 633: securityonion-elsa-extras: parse ssl_version and ssl_cipher out of Bro ssl.log
https://code.google.com/p/security-onion/issues/detail?id=633
Updating
The new packages are now available in our stable repo. Please see the following page for full update instructions:
https://code.google.com/p/security-onion/wiki/Upgrade
Thanks
Thanks to Lee Sharp for providing the new collapsible query categories!
Thanks to Eddy Simons and David Zawdie for testing!
Feedback
If you have any questions or problems, please use our security-onion mailing list:
https://code.google.com/p/security-onion/wiki/MailingLists
Commercial Support
Need commercial support? Please see:
http://securityonionsolutions.com
Help Wanted
If you and/or your organization have found value in Security Onion, please consider giving back to the community by joining one of our teams:
https://code.google.com/p/security-onion/wiki/TeamMembers
We especially need help in answering support questions on the mailing list:
http://groups.google.com/group/security-onion
We also need help testing new packages:
http://groups.google.com/group/security-onion-testing
Thanks!
http://googleonlinesecurity.blogspot.com/2014/10/this-poodle-bites-exploiting-ssl-30.html
http://www.wired.com/2014/10/poodle-explained/
https://isc.sans.edu/diary/OpenSSL%3A+SSLv3+POODLE+Vulnerability+Official+Release/18827
https://www.imperialviolet.org/2014/10/14/poodle.html
In response to this, we recently added some SSLv3 queries:
http://blog.securityonion.net/2014/10/new-securityonion-web-page-package-adds.html
Today, we're adding some additional ELSA queries to allow you to see your SSL traffic grouped by version or by cipher.
 |
| SSL - Top SSL Versions |
 |
| SSL - Top SSL Ciphers |
Today's update will also reconfigure Security Onion's Apache instance to no longer accept connections using SSLv3.
The new package versions are as follows:
securityonion-elsa-extras - 20131117-1ubuntu0securityonion45
securityonion-web-page - 20141015-0ubuntu0securityonion2
Issues Resolved
Issue 629: securityonion-web-page: disable SSLv3 in Apache ssl.conf
https://code.google.com/p/security-onion/issues/detail?id=629
Issue 627: securityonion-web-page: separate syslog-ng into program and host queries
https://code.google.com/p/security-onion/issues/detail?id=627
Issue 631: securityonion-web-page: collapse query categories by default
https://code.google.com/p/security-onion/issues/detail?id=631
Issue 634: securityonion-web-page: add queries for ssl_version and ssl_cipher
https://code.google.com/p/security-onion/issues/detail?id=634
Issue 633: securityonion-elsa-extras: parse ssl_version and ssl_cipher out of Bro ssl.log
https://code.google.com/p/security-onion/issues/detail?id=633
Updating
The new packages are now available in our stable repo. Please see the following page for full update instructions:
https://code.google.com/p/security-onion/wiki/Upgrade
 |
| Updating with "sudo soup" |
 |
| Restarting Apache with "sudo service apache2 restart" |
 |
| Verifying that Apache no longer accepts SSLv3 connections |
Thanks
Thanks to Lee Sharp for providing the new collapsible query categories!
Thanks to Eddy Simons and David Zawdie for testing!
Feedback
If you have any questions or problems, please use our security-onion mailing list:
https://code.google.com/p/security-onion/wiki/MailingLists
Commercial Support
Need commercial support? Please see:
http://securityonionsolutions.com
Help Wanted
If you and/or your organization have found value in Security Onion, please consider giving back to the community by joining one of our teams:
https://code.google.com/p/security-onion/wiki/TeamMembers
We especially need help in answering support questions on the mailing list:
http://groups.google.com/group/security-onion
We also need help testing new packages:
http://groups.google.com/group/security-onion-testing
Thanks!
Wednesday, October 15, 2014
New securityonion-web-page package adds queries to monitor SSLv3
A vulnerability in SSLv3 was recently announced (nicknamed POODLE):
http://googleonlinesecurity.blogspot.com/2014/10/this-poodle-bites-exploiting-ssl-30.html
http://www.wired.com/2014/10/poodle-explained/
https://isc.sans.edu/diary/OpenSSL%3A+SSLv3+POODLE+Vulnerability+Official+Release/18827
https://www.imperialviolet.org/2014/10/14/poodle.html
I've added a couple of ELSA queries to help you monitor your network for SSLv3:
The new package version is as follows:
securityonion-web-page - 20120722-0ubuntu0securityonion26
Issues Resolved
Issue 628: securityonion-web-page: add ELSA queries for SSLv3
https://code.google.com/p/security-onion/issues/detail?id=628
Updating
The new package is now available in our stable repo. Please see the following page for full update instructions:
https://code.google.com/p/security-onion/wiki/Upgrade
Feedback
If you have any questions or problems, please use our security-onion mailing list:
https://code.google.com/p/security-onion/wiki/MailingLists
Training
Tomorrow is the LAST day to sign up for the 3-day Security Onion class in Richmond VA!
https://security-onion-class-20141020.eventbrite.com/
Commercial Support
Need commercial support? Please see:
http://securityonionsolutions.com
Help Wanted
If you and/or your organization have found value in Security Onion, please consider giving back to the community by joining one of our teams:
https://code.google.com/p/security-onion/wiki/TeamMembers
We especially need help in answering support questions on the mailing list:
http://groups.google.com/group/security-onion
We also need help testing new packages:
http://groups.google.com/group/security-onion-testing
Thanks!
http://googleonlinesecurity.blogspot.com/2014/10/this-poodle-bites-exploiting-ssl-30.html
http://www.wired.com/2014/10/poodle-explained/
https://isc.sans.edu/diary/OpenSSL%3A+SSLv3+POODLE+Vulnerability+Official+Release/18827
https://www.imperialviolet.org/2014/10/14/poodle.html
I've added a couple of ELSA queries to help you monitor your network for SSLv3:
 |
| SSL - Top SSLv3 DST IPs |
The new package version is as follows:
securityonion-web-page - 20120722-0ubuntu0securityonion26
Issues Resolved
Issue 628: securityonion-web-page: add ELSA queries for SSLv3
https://code.google.com/p/security-onion/issues/detail?id=628
Updating
The new package is now available in our stable repo. Please see the following page for full update instructions:
https://code.google.com/p/security-onion/wiki/Upgrade
Feedback
If you have any questions or problems, please use our security-onion mailing list:
https://code.google.com/p/security-onion/wiki/MailingLists
Training
Tomorrow is the LAST day to sign up for the 3-day Security Onion class in Richmond VA!
https://security-onion-class-20141020.eventbrite.com/
Commercial Support
Need commercial support? Please see:
http://securityonionsolutions.com
Help Wanted
If you and/or your organization have found value in Security Onion, please consider giving back to the community by joining one of our teams:
https://code.google.com/p/security-onion/wiki/TeamMembers
We especially need help in answering support questions on the mailing list:
http://groups.google.com/group/security-onion
We also need help testing new packages:
http://groups.google.com/group/security-onion-testing
Thanks!
Monday, October 6, 2014
OSSEC 2.8.1
OSSEC 2.8.1 was recently released:
http://www.ossec.net/?p=1135
Notice in the comments there is an additional patch which has now been applied to OSSEC on github:
https://github.com/ossec/ossec-hids/pull/315
I've packaged OSSEC 2.8.1 (with the patch from github) and also fixed a performance issue in our OSSEC configuration. Our OSSEC configuration now uses a new script called /usr/bin/sostat-interface to detect if an interface hasn't received any packets within a specific time interval (10 minutes by default).
The new package versions are as follows:
ossec-hids-server - 2.8.1-ubuntu10securityonion8
securityonion-sostat - 20120722-0ubuntu0securityonion31
The new packages have been tested by the following (thanks!):
David Zawdie
UPDATE 20141006 13:01
Scott F. found an issue in the postinst script:
https://groups.google.com/d/topic/security-onion/5LbonKad-88/discussion
This issue has been resolved and additional error handling has been added. The new package version is:
ossec-hids-server - 2.8.1-ubuntu10securityonion10
Issue 589: OSSEC 2.8.1
https://code.google.com/p/security-onion/issues/detail?id=589
Issue 621: sostat: add sostat-interface
https://code.google.com/p/security-onion/issues/detail?id=621
Updating
The new packages are now available in our stable repo. Please see the following page for full update instructions:
https://code.google.com/p/security-onion/wiki/Upgrade
After installing the new OSSEC package, you'll need to double-check /var/ossec/etc/ossec.conf and add back any local customizations. You can then restart OSSEC as follows:
Screenshots
Feedback
If you have any questions or problems, please use our security-onion mailing list:
https://code.google.com/p/security-onion/wiki/MailingLists
Training
Only 13 seats left for the 3-day Security Onion class in Richmond VA!
https://security-onion-class-20141020.eventbrite.com/
Commercial Support
Need commercial support? Please see:
http://securityonionsolutions.com
Help Wanted
If you and/or your organization have found value in Security Onion, please consider giving back to the community by joining one of our teams:
https://code.google.com/p/security-onion/wiki/TeamMembers
We especially need help in answering support questions on the mailing list:
http://groups.google.com/group/security-onion
We also need help testing new packages:
http://groups.google.com/group/security-onion-testing
Thanks!
http://www.ossec.net/?p=1135
Notice in the comments there is an additional patch which has now been applied to OSSEC on github:
https://github.com/ossec/ossec-hids/pull/315
I've packaged OSSEC 2.8.1 (with the patch from github) and also fixed a performance issue in our OSSEC configuration. Our OSSEC configuration now uses a new script called /usr/bin/sostat-interface to detect if an interface hasn't received any packets within a specific time interval (10 minutes by default).
The new package versions are as follows:
ossec-hids-server - 2.8.1-ubuntu10securityonion8
securityonion-sostat - 20120722-0ubuntu0securityonion31
The new packages have been tested by the following (thanks!):
David Zawdie
UPDATE 20141006 13:01
Scott F. found an issue in the postinst script:
https://groups.google.com/d/topic/security-onion/5LbonKad-88/discussion
This issue has been resolved and additional error handling has been added. The new package version is:
ossec-hids-server - 2.8.1-ubuntu10securityonion10
Issues Resolved
Issue 589: OSSEC 2.8.1
https://code.google.com/p/security-onion/issues/detail?id=589
Issue 621: sostat: add sostat-interface
https://code.google.com/p/security-onion/issues/detail?id=621
Updating
The new packages are now available in our stable repo. Please see the following page for full update instructions:
https://code.google.com/p/security-onion/wiki/Upgrade
After installing the new OSSEC package, you'll need to double-check /var/ossec/etc/ossec.conf and add back any local customizations. You can then restart OSSEC as follows:
sudo service ossec-hids-server restart
Screenshots
 |
| Update Process |
 |
| After updating, add back any local customization to ossec.conf and then run "sudo service ossec-hids-server restart" |
 |
| OSSEC now runs /usr/bin/sostat-interface every 10 minutes to check for interfaces not receiving any traffic |
 |
| When OSSEC sees that an interface hasn't received any packets, it alerts |
 |
| OSSEC alert in Sguil |
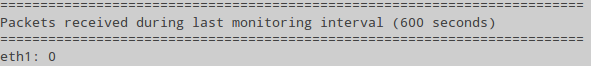 |
| sostat now reports on the number of packets received during the last monitoring interval |
Feedback
If you have any questions or problems, please use our security-onion mailing list:
https://code.google.com/p/security-onion/wiki/MailingLists
Training
Only 13 seats left for the 3-day Security Onion class in Richmond VA!
https://security-onion-class-20141020.eventbrite.com/
Commercial Support
Need commercial support? Please see:
http://securityonionsolutions.com
Help Wanted
If you and/or your organization have found value in Security Onion, please consider giving back to the community by joining one of our teams:
https://code.google.com/p/security-onion/wiki/TeamMembers
We especially need help in answering support questions on the mailing list:
http://groups.google.com/group/security-onion
We also need help testing new packages:
http://groups.google.com/group/security-onion-testing
Thanks!
Wednesday, October 1, 2014
New securityonion-bro-scripts and securityonion-web-page packages
As mentioned previously, Seth Hall has developed some comprehensive ShellShock detection scripts for Bro:
https://github.com/broala/bro-shellshock
http://blog.securityonion.net/2014/09/bash-vulnerability-part-3.html
http://blog.securityonion.net/2014/09/new-securityonion-bro-scripts.html
http://blog.securityonion.net/2014/09/securityonion-bro-scripts-now-detects.html
Seth has updated these scripts again today to "Add shellscripts as a post-exploit detection mechanism.":
https://github.com/broala/bro-shellshock/commit/4be009f9b7bf8ce9b99533cb4c7b8dd76aba87b7
I've updated the securityonion-bro-scripts package to include these changes. I've also updated the securityonion-web-page package to include some ELSA queries for "ShellShock Exploits" and "ShellShock Scanners".
New package versions:
securityonion-bro-scripts - 20121004-0ubuntu0securityonion38
securityonion-web-page - 20120722-0ubuntu0securityonion25
Issues Resolved
Issue 618: securityonion-bro-scripts: ShellShock Add shellscripts as a post-exploit detection mechanism
https://code.google.com/p/security-onion/issues/detail?id=618
Issue 617: securityonion-web-page: add queries for Bro ShellShock Notices
https://code.google.com/p/security-onion/issues/detail?id=617
Issue 583: securityonion-web-page: update "All OSSEC Logs" query
https://code.google.com/p/security-onion/issues/detail?id=583
Issue 599: securityonion-web-page: highlight current ELSA query
https://code.google.com/p/security-onion/issues/detail?id=599
Updating
The new packages are now available in our stable repo. Please see the following page for full update instructions:
https://code.google.com/p/security-onion/wiki/Upgrade
To apply the new Bro ShellShock detection, you'll need to restart Bro as follows:
Screenshots
Feedback
If you have any questions or problems, please use our security-onion mailing list:
https://code.google.com/p/security-onion/wiki/MailingLists
Training
Only 15 seats left for the 3-day Security Onion class in Richmond VA!
https://security-onion-class-20141020.eventbrite.com/
Commercial Support
Need commercial support? Please see:
http://securityonionsolutions.com
Help Wanted
If you and/or your organization have found value in Security Onion, please consider giving back to the community by joining one of our teams:
https://code.google.com/p/security-onion/wiki/TeamMembers
We especially need help in answering support questions on the mailing list:
http://groups.google.com/group/security-onion
We also need help testing new packages:
http://groups.google.com/group/security-onion-testing
Thanks!
"This script detects successful exploitation of the Bash vulnerability with CVE-2014-6271 nicknamed "ShellShock". It's more comprehensive than most of the detections around in that it's watching for behavior from the attacked host that might indicate successful compromise or actual vulnerability."
https://github.com/broala/bro-shellshock
http://blog.securityonion.net/2014/09/bash-vulnerability-part-3.html
http://blog.securityonion.net/2014/09/new-securityonion-bro-scripts.html
http://blog.securityonion.net/2014/09/securityonion-bro-scripts-now-detects.html
Seth has updated these scripts again today to "Add shellscripts as a post-exploit detection mechanism.":
https://github.com/broala/bro-shellshock/commit/4be009f9b7bf8ce9b99533cb4c7b8dd76aba87b7
I've updated the securityonion-bro-scripts package to include these changes. I've also updated the securityonion-web-page package to include some ELSA queries for "ShellShock Exploits" and "ShellShock Scanners".
New package versions:
securityonion-bro-scripts - 20121004-0ubuntu0securityonion38
securityonion-web-page - 20120722-0ubuntu0securityonion25
Issues Resolved
Issue 618: securityonion-bro-scripts: ShellShock Add shellscripts as a post-exploit detection mechanism
https://code.google.com/p/security-onion/issues/detail?id=618
Issue 617: securityonion-web-page: add queries for Bro ShellShock Notices
https://code.google.com/p/security-onion/issues/detail?id=617
Issue 583: securityonion-web-page: update "All OSSEC Logs" query
https://code.google.com/p/security-onion/issues/detail?id=583
Issue 599: securityonion-web-page: highlight current ELSA query
https://code.google.com/p/security-onion/issues/detail?id=599
Updating
The new packages are now available in our stable repo. Please see the following page for full update instructions:
https://code.google.com/p/security-onion/wiki/Upgrade
To apply the new Bro ShellShock detection, you'll need to restart Bro as follows:
sudo nsm_sensor_ps-restart --only-bro
Screenshots
 |
| Update Process |
 |
| Restarting Bro with "sudo nsm_sensor_ps-restart --only-bro" |
 |
| New ELSA Query for Notice - ShellShock Exploits |
 |
| New ELSA Query for Notice - ShellShock Scanners |
Feedback
If you have any questions or problems, please use our security-onion mailing list:
https://code.google.com/p/security-onion/wiki/MailingLists
Training
Only 15 seats left for the 3-day Security Onion class in Richmond VA!
https://security-onion-class-20141020.eventbrite.com/
Commercial Support
Need commercial support? Please see:
http://securityonionsolutions.com
Help Wanted
If you and/or your organization have found value in Security Onion, please consider giving back to the community by joining one of our teams:
https://code.google.com/p/security-onion/wiki/TeamMembers
We especially need help in answering support questions on the mailing list:
http://groups.google.com/group/security-onion
We also need help testing new packages:
http://groups.google.com/group/security-onion-testing
Thanks!
Tuesday, September 30, 2014
securityonion-bro-scripts now detects the ShellShock Qmail SMTP "MAIL FROM" attack vector
Seth Hall added support for the ShellShock Qmail SMTP "MAIL FROM" attack vector to his Bro ShellShock scripts:
https://github.com/broala/bro-shellshock/commit/6ba280179e86243ecc0ed0b84d38e5906bbdcadc
I've updated the securityonion-bro-scripts package to include these changes.
New package version:
securityonion-bro-scripts - 20121004-0ubuntu0securityonion37
Issues Resolved
Issue 616: securityonion-bro-scripts: ShellShock Qmail SMTP "MAIL FROM" attack vector
https://code.google.com/p/security-onion/issues/detail?id=616
Updating
The new package is now available in our stable repo. Please see the following page for full update instructions:
https://code.google.com/p/security-onion/wiki/Upgrade
To apply the new Bro ShellShock detection, you'll need to restart Bro as follows:
Screenshots
Feedback
If you have any questions or problems, please use our security-onion mailing list:
https://code.google.com/p/security-onion/wiki/MailingLists
Training
Only 16 seats left for the 3-day Security Onion class in Richmond VA!
https://security-onion-class-20141020.eventbrite.com/
Commercial Support
Need commercial support? Please see:
http://securityonionsolutions.com
Help Wanted
If you and/or your organization have found value in Security Onion, please consider giving back to the community by joining one of our teams:
https://code.google.com/p/security-onion/wiki/TeamMembers
We especially need help in answering support questions on the mailing list:
http://groups.google.com/group/security-onion
We also need help testing new packages:
http://groups.google.com/group/security-onion-testing
Thanks!
https://github.com/broala/bro-shellshock/commit/6ba280179e86243ecc0ed0b84d38e5906bbdcadc
I've updated the securityonion-bro-scripts package to include these changes.
New package version:
securityonion-bro-scripts - 20121004-0ubuntu0securityonion37
Issues Resolved
Issue 616: securityonion-bro-scripts: ShellShock Qmail SMTP "MAIL FROM" attack vector
https://code.google.com/p/security-onion/issues/detail?id=616
Updating
The new package is now available in our stable repo. Please see the following page for full update instructions:
https://code.google.com/p/security-onion/wiki/Upgrade
To apply the new Bro ShellShock detection, you'll need to restart Bro as follows:
sudo nsm_sensor_ps-restart --only-bro
Screenshots
 |
| Update Process |
 |
| Restarting Bro to load new ShellShock detection |
Feedback
If you have any questions or problems, please use our security-onion mailing list:
https://code.google.com/p/security-onion/wiki/MailingLists
Training
Only 16 seats left for the 3-day Security Onion class in Richmond VA!
https://security-onion-class-20141020.eventbrite.com/
Commercial Support
Need commercial support? Please see:
http://securityonionsolutions.com
Help Wanted
If you and/or your organization have found value in Security Onion, please consider giving back to the community by joining one of our teams:
https://code.google.com/p/security-onion/wiki/TeamMembers
We especially need help in answering support questions on the mailing list:
http://groups.google.com/group/security-onion
We also need help testing new packages:
http://groups.google.com/group/security-onion-testing
Thanks!
Suricata 2.0.4
Suricata 2.0.4 was recently released:
http://www.openinfosecfoundation.org/index.php/component/content/article/1-latest-news/198-suricata-204-available
I've packaged Suricata 2.0.4 and it has been tested by David Zawdie (thanks!).
The new package version is:
securityonion-suricata - 2.0.4-0ubuntu0securityonion1
Issues Resolved
Issue 600: Suricata 2.0.4
https://code.google.com/p/security-onion/issues/detail?id=600
Updating
The new packages are now available in our stable repo. Please see the following page for full update instructions:
https://code.google.com/p/security-onion/wiki/Upgrade
This update will back up each of your existing suricata.yaml files to suricata.yaml.bak. You'll then need to do the following:
Screenshots
Feedback
If you have any questions or problems, please use our security-onion mailing list:
https://code.google.com/p/security-onion/wiki/MailingLists
Training
Only 16 seats left for the 3-day Security Onion class in Richmond VA!
https://security-onion-class-20141020.eventbrite.com/
Commercial Support
Need commercial support? Please see:
http://securityonionsolutions.com
Help Wanted
If you and/or your organization have found value in Security Onion, please consider giving back to the community by joining one of our teams:
https://code.google.com/p/security-onion/wiki/TeamMembers
We especially need help in answering support questions on the mailing list:
http://groups.google.com/group/security-onion
We also need help testing new packages:
http://groups.google.com/group/security-onion-testing
Thanks!
http://www.openinfosecfoundation.org/index.php/component/content/article/1-latest-news/198-suricata-204-available
I've packaged Suricata 2.0.4 and it has been tested by David Zawdie (thanks!).
The new package version is:
securityonion-suricata - 2.0.4-0ubuntu0securityonion1
Issues Resolved
Issue 600: Suricata 2.0.4
https://code.google.com/p/security-onion/issues/detail?id=600
Updating
The new packages are now available in our stable repo. Please see the following page for full update instructions:
https://code.google.com/p/security-onion/wiki/Upgrade
This update will back up each of your existing suricata.yaml files to suricata.yaml.bak. You'll then need to do the following:
- re-apply any local customizations to suricata.yaml
- update ruleset and restart Suricata as follows:
sudo rule-update
Screenshots
 |
| Update Process |
 |
| sudo rule-update |
 |
| rule-update restarts Suricata |
Feedback
If you have any questions or problems, please use our security-onion mailing list:
https://code.google.com/p/security-onion/wiki/MailingLists
Training
Only 16 seats left for the 3-day Security Onion class in Richmond VA!
https://security-onion-class-20141020.eventbrite.com/
Commercial Support
Need commercial support? Please see:
http://securityonionsolutions.com
Help Wanted
If you and/or your organization have found value in Security Onion, please consider giving back to the community by joining one of our teams:
https://code.google.com/p/security-onion/wiki/TeamMembers
We especially need help in answering support questions on the mailing list:
http://groups.google.com/group/security-onion
We also need help testing new packages:
http://groups.google.com/group/security-onion-testing
Thanks!
Monday, September 29, 2014
New Setup package adds Snort Community Ruleset to VRT Ruleset
On Friday, I wrote a quick blog post about the ShellShock rules in the Snort Community ruleset:
http://blog.securityonion.net/2014/09/bash-vulnerability-part-5-shellshock.html
The new version of Setup mentioned in that blog post has been tested by Eddy Simons (thanks!) and is now available in our stable PPA.
New package versions:
securityonion-setup - 20120912-0ubuntu0securityonion122
Issues Resolved
Issue 613: Setup: if user chooses VRT rules, enable Community as well
https://code.google.com/p/security-onion/issues/detail?id=613
Updating
The new packages are now available in our stable repo. Please see the following page for full update instructions:
https://code.google.com/p/security-onion/wiki/Upgrade
Screenshots
Feedback
If you have any questions or problems, please use our security-onion mailing list:
https://code.google.com/p/security-onion/wiki/MailingLists
Training
Only 17 seats left for the 3-day Security Onion class in Richmond VA!
https://security-onion-class-20141020.eventbrite.com/
Commercial Support
Need commercial support? Please see:
http://securityonionsolutions.com
Help Wanted
If you and/or your organization have found value in Security Onion, please consider giving back to the community by joining one of our teams:
https://code.google.com/p/security-onion/wiki/TeamMembers
We especially need help in answering support questions on the mailing list:
http://groups.google.com/group/security-onion
We also need help testing new packages:
http://groups.google.com/group/security-onion-testing
Thanks!
http://blog.securityonion.net/2014/09/bash-vulnerability-part-5-shellshock.html
The new version of Setup mentioned in that blog post has been tested by Eddy Simons (thanks!) and is now available in our stable PPA.
New package versions:
securityonion-setup - 20120912-0ubuntu0securityonion122
Issues Resolved
Issue 613: Setup: if user chooses VRT rules, enable Community as well
https://code.google.com/p/security-onion/issues/detail?id=613
Updating
The new packages are now available in our stable repo. Please see the following page for full update instructions:
https://code.google.com/p/security-onion/wiki/Upgrade
Screenshots
 |
| Update Process |
 |
| ShellShock alert in Snorby |
If you have any questions or problems, please use our security-onion mailing list:
https://code.google.com/p/security-onion/wiki/MailingLists
Training
Only 17 seats left for the 3-day Security Onion class in Richmond VA!
https://security-onion-class-20141020.eventbrite.com/
Commercial Support
Need commercial support? Please see:
http://securityonionsolutions.com
Help Wanted
If you and/or your organization have found value in Security Onion, please consider giving back to the community by joining one of our teams:
https://code.google.com/p/security-onion/wiki/TeamMembers
We especially need help in answering support questions on the mailing list:
http://groups.google.com/group/security-onion
We also need help testing new packages:
http://groups.google.com/group/security-onion-testing
Thanks!
Saturday, September 27, 2014
Bash Vulnerability Part 6: YABU - Yet Another Bash Update
This is a continuation of the ShellShock posts from the last few days:
http://blog.securityonion.net/2014/09/bash-vulnerability.html
http://blog.securityonion.net/2014/09/bash-vulnerability-part-2.html
http://blog.securityonion.net/2014/09/bash-vulnerability-part-3.html
http://blog.securityonion.net/2014/09/bash-vulnerability-part-4-another.html
http://blog.securityonion.net/2014/09/bash-vulnerability-part-5-shellshock.html
http://blog.securityonion.net/2014/09/new-securityonion-bro-scripts.html
Ubuntu has now released yet another bash update:
http://www.ubuntu.com/usn/usn-2364-1/
You should install this updated package as soon as possible. As always, we recommend using "soup" to apply package updates. Please see the following page for full update instructions:
https://code.google.com/p/security-onion/wiki/Upgrade
If you have any questions or problems, please use our security-onion mailing list:
https://code.google.com/p/security-onion/wiki/MailingLists
Friday, September 26, 2014
New securityonion-bro-scripts, securityonion-onionsalt, and salt packages
I've updated the securityonion-bro-scripts package to include Seth Hall's ShellShock detector from here:
https://github.com/broala/bro-shellshock
securityonion-bro-scripts also creates a new directory called /opt/bro/share/bro/intel/ that makes it easy for you to add intel to the Bro Intel framework.
Mike Reeves, Ryan Peck, and I have updated the OnionSalt scripts to replicate more data from master to sensor. This includes the /opt/bro/share/bro/intel/ directory mentioned above and also OSSEC's agent.conf and local_decoder.xml files.
Finally, SaltStack has updated their salt packages, so we include that as well.
New package versions:
salt - 2014.1.10-1precise1
securityonion-bro-scripts - 20121004-0ubuntu0securityonion36
securityonion-onionsalt - 20140917-0ubuntu0securityonion17
These new packages have been tested by the following (thanks!):
Brian Kellogg
Rob C
Issues Resolved:
Issue 612: securityonion-bro-scripts: include ShellShock detection
https://code.google.com/p/security-onion/issues/detail?id=612
Issue 606: securityonion-bro-scripts: create /opt/bro/share/bro/intel/
with example intel
https://code.google.com/p/security-onion/issues/detail?id=606
Issue 609: Onionsalt should copy /opt/bro/share/bro/intel/
https://code.google.com/p/security-onion/issues/detail?id=609
Issue 580: onionsalt should copy OSSEC agent.conf and local_decoder.xml
https://code.google.com/p/security-onion/issues/detail?id=580
Issue 579: Update salt
https://code.google.com/p/security-onion/issues/detail?id=579
Updating
The new packages are now available in our stable repo. Please see the following page for full update instructions:
https://code.google.com/p/security-onion/wiki/Upgrade
To apply the new Bro ShellShock detection, you'll need to restart Bro as follows:
Screenshots
Feedback
If you have any questions or problems, please use our security-onion mailing list:
https://code.google.com/p/security-onion/wiki/MailingLists
Training
Only 17 seats left for the 3-day Security Onion class in Richmond VA!
https://security-onion-class-20141020.eventbrite.com/
Commercial Support
Need commercial support? Please see:
http://securityonionsolutions.com
Help Wanted
If you and/or your organization have found value in Security Onion, please consider giving back to the community by joining one of our teams:
https://code.google.com/p/security-onion/wiki/TeamMembers
We especially need help in answering support questions on the mailing list:
http://groups.google.com/group/security-onion
We also need help testing new packages:
http://groups.google.com/group/security-onion-testing
Thanks!
UPDATE 20140927 08:00
Please see:
http://blog.securityonion.net/2014/09/bash-vulnerability-part-6-yabu-yet.html
https://github.com/broala/bro-shellshock
securityonion-bro-scripts also creates a new directory called /opt/bro/share/bro/intel/ that makes it easy for you to add intel to the Bro Intel framework.
Mike Reeves, Ryan Peck, and I have updated the OnionSalt scripts to replicate more data from master to sensor. This includes the /opt/bro/share/bro/intel/ directory mentioned above and also OSSEC's agent.conf and local_decoder.xml files.
Finally, SaltStack has updated their salt packages, so we include that as well.
New package versions:
salt - 2014.1.10-1precise1
securityonion-bro-scripts - 20121004-0ubuntu0securityonion36
securityonion-onionsalt - 20140917-0ubuntu0securityonion17
These new packages have been tested by the following (thanks!):
Brian Kellogg
Rob C
Issues Resolved:
Issue 612: securityonion-bro-scripts: include ShellShock detection
https://code.google.com/p/security-onion/issues/detail?id=612
Issue 606: securityonion-bro-scripts: create /opt/bro/share/bro/intel/
with example intel
https://code.google.com/p/security-onion/issues/detail?id=606
Issue 609: Onionsalt should copy /opt/bro/share/bro/intel/
https://code.google.com/p/security-onion/issues/detail?id=609
Issue 580: onionsalt should copy OSSEC agent.conf and local_decoder.xml
https://code.google.com/p/security-onion/issues/detail?id=580
Issue 579: Update salt
https://code.google.com/p/security-onion/issues/detail?id=579
Updating
The new packages are now available in our stable repo. Please see the following page for full update instructions:
https://code.google.com/p/security-onion/wiki/Upgrade
To apply the new Bro ShellShock detection, you'll need to restart Bro as follows:
sudo nsm_sensor_ps-restart --only-bro
Screenshots
 |
| Update Process |
 |
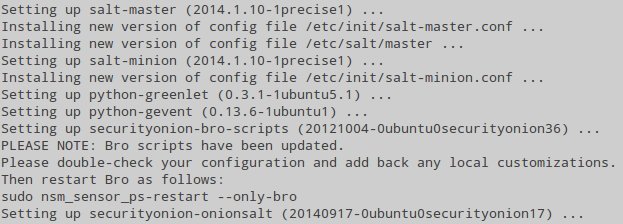
| Restarting Bro to load new ShellShock Detection |
 |
| /opt/bro/share/bro/ now contains intel/ and shellshock/ directories |
 |
| Bro ShellShock logs (http.log and notice.log) |
Feedback
If you have any questions or problems, please use our security-onion mailing list:
https://code.google.com/p/security-onion/wiki/MailingLists
Training
Only 17 seats left for the 3-day Security Onion class in Richmond VA!
https://security-onion-class-20141020.eventbrite.com/
Commercial Support
Need commercial support? Please see:
http://securityonionsolutions.com
Help Wanted
If you and/or your organization have found value in Security Onion, please consider giving back to the community by joining one of our teams:
https://code.google.com/p/security-onion/wiki/TeamMembers
We especially need help in answering support questions on the mailing list:
http://groups.google.com/group/security-onion
We also need help testing new packages:
http://groups.google.com/group/security-onion-testing
Thanks!
UPDATE 20140927 08:00
Please see:
http://blog.securityonion.net/2014/09/bash-vulnerability-part-6-yabu-yet.html
Subscribe to:
Posts (Atom)